Do you monitor your application for dependency vulnerabilities?
Loading last updated info...
Efficient software developers don't reinvent the wheel and know the right packages to use when monitoring vulnerabilities in both frontend and backend packages.
Using a bunch of third-party libraries as the supporting building blocks to build modern, high-quality applications became a common practice since they save time and money in full-stack projects.
But this comes with an unexpected side effect: out-of-date packages that must be updated and re-tested, and even worse, vulnerabilities can be introduced!
One of the big challenges for developers to address is when a project has been delivered to a client and gone into maintenance mode. With no developer actively working on the project, if a vulnerability is discovered in a library referenced in the project, no one will be aware of it, and it will cause pain.
However, if you monitor the packages you have installed, and a vulnerability is reported, then as developers, we have a duty of care to inform our clients.
What should you monitor?
Monitor every dependency source used by your application, including:
- npm, NuGet, Maven, Gradle, pip and other package ecosystem
- Transitive dependencies (dependencies of dependencies)
- Container base images
- GitHub Actions and other CI/CD dependencies
Level 0 - Manual tracking (not recommended)
A developer can manually list packages and search vulnerability databases such as the GitHub Advisory Database.
This approach is slow, inconsistent, and usually stops once active development finishes.
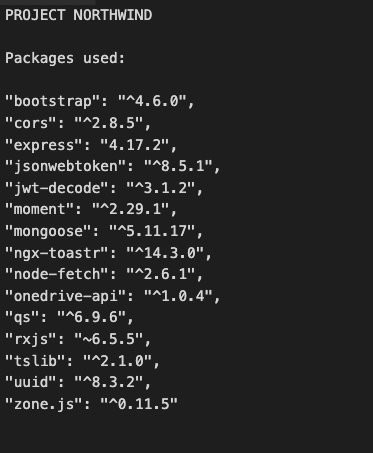
❌ Figure: Bad example - Tracking list of packages manually
Level 1 - Running local vulnerability scans
Modern package managers such as npm or NuGet offers a way to check for vulnerabilities in the installed libraries.
See Do you keep your npm and Yarn packages up to date?
- npm:
npm audit - yarn:
yarn audit - dotnet cli:
dotnet list package --vulnerable
Regularly running this command can give a summarised report on known vulnerabilities in the referenced libraries.
This is an improvement over manual tracking but still requires a developer to check out the latest code and then run the command.
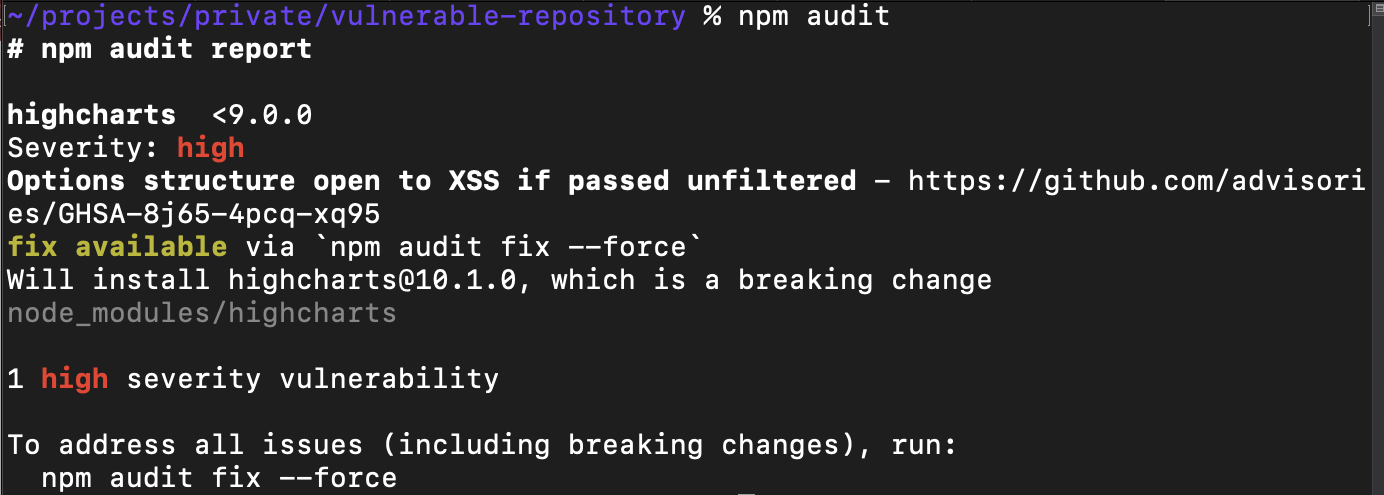
🙂 Figure: OK example - This npm audit command informs that there is 1 package with a high severity vulnerability
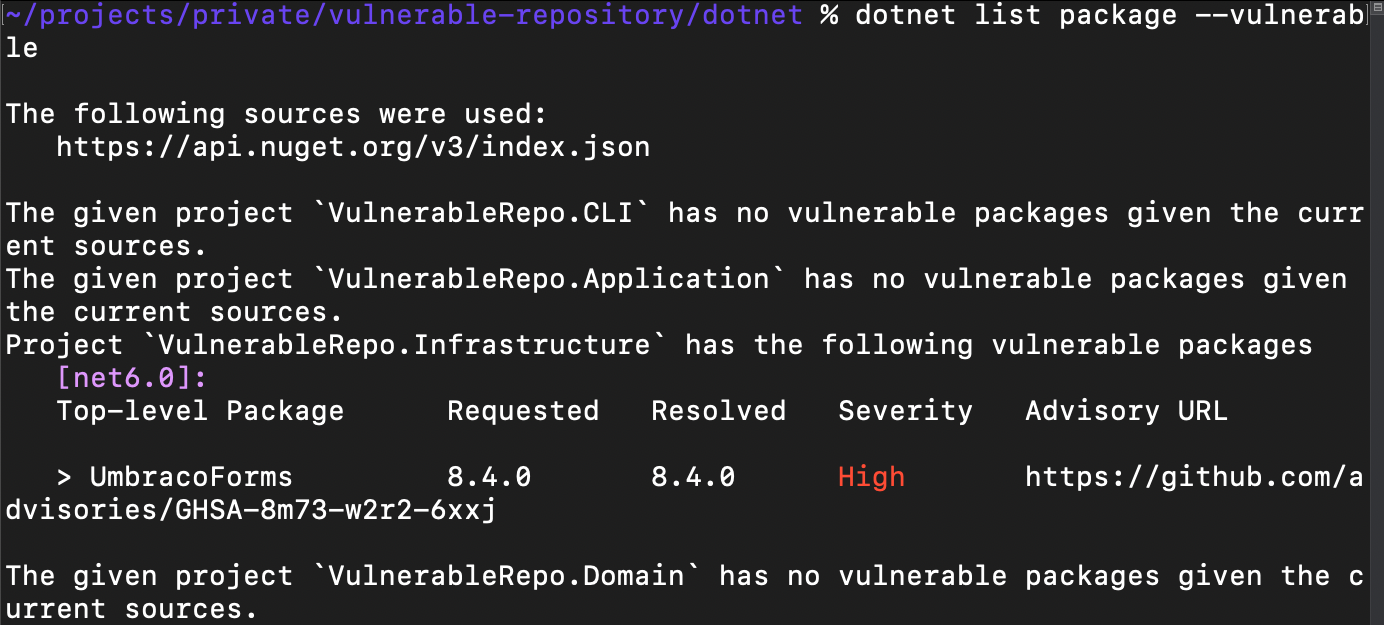
🙂 Figure: OK example - This dotnet command informs that there is 1 package with a high severity vulnerability
Level 2 - Automate vulnerability scanning (recommended)
Using 3rd party tools can help you to automate vulnerability scanning.
These tools will alert you whenever there's a security vulnerability detected in the project and optionally raise a PR for it.
Some of the available tools in the market:
- Dependabot - free for all repositories under GitHub, easy to set up in the repository settings (recommended). Used in SSW Rules and TinaCMS
- Mend Renovate - free, works beyond GitHub (Azure DevOps, GitLab) and across NuGet, npm, pip and Docker. More configurable than Dependabot, with grouped PRs and auto-merge
- GitHub Enterprise Advanced Security - $ includes Dependabot plus additional features like code scanning. See here for more details.
- Snyk - $
- Sonatype - $
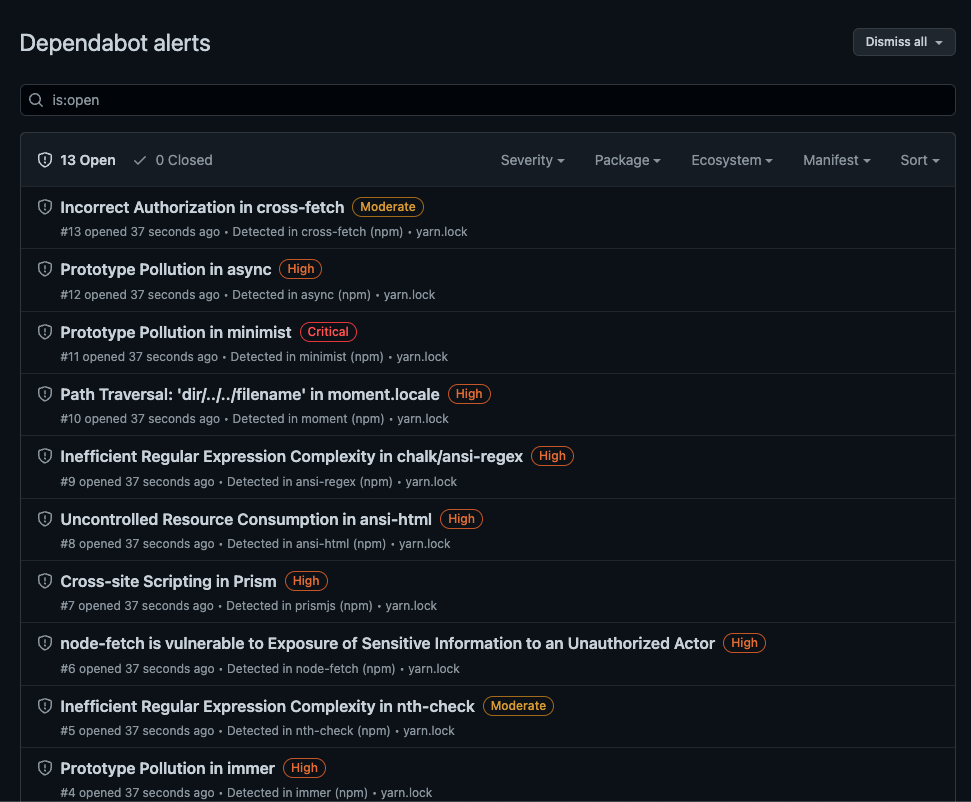
✅ Figure: Good example - Dependabot produces a vulnerability report periodically (and can raise a PR for you)
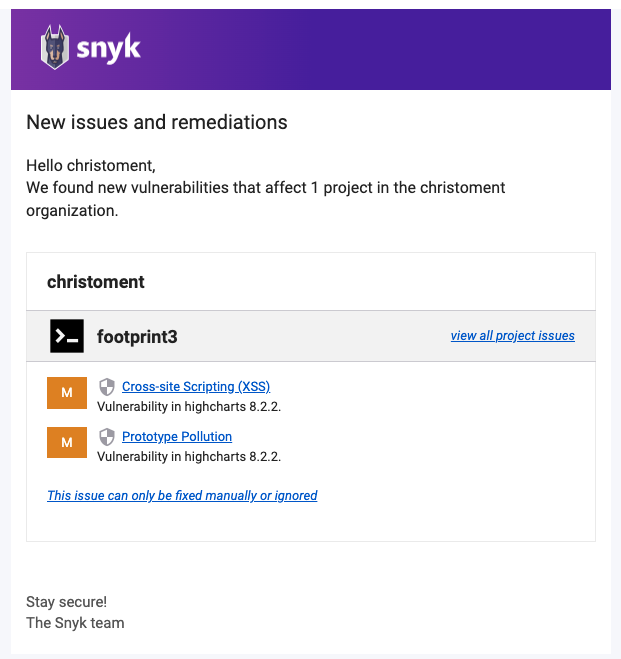
✅ Figure: Good example - Snyk produces a vulnerability detection alert email
Level 3 - Preventing vulnerable dependencies from being merged
Monitoring existing dependencies is not half of the job, your pull requests should also be checked for newly introduced vulnerabilities.
For GitHub repositories, use the Dependency Review Action as apart of your CI. This prevents a pull request from adding a dependency with a known high or critical vulnerability.
Note: The Dependency Review Action only works on public repositories, or private repositories with GitHub Advanced Security enabled. On a private repository without it, the action will fail the build.
name: Dependency Reviewon:pull_request:permissions:contents: readjobs:dependency-review:runs-on: ubuntu-lateststeps:- uses: actions/checkout@v6- uses: actions/dependency-review-action@v5with:fail-on-severity: high
Figure: Who's better at fighting the vulnerabilities?